Get the last Reboot or Shutdown reason and user from the Windows Event Log


Start by going into Event Viewer (Windows+R or the Start Menu and type eventvwr.msc).  Navigate to the System Log under Windows, we then want to use Filter Current Log to allow us to only show Events with certain attributes (such as Source or IDs).
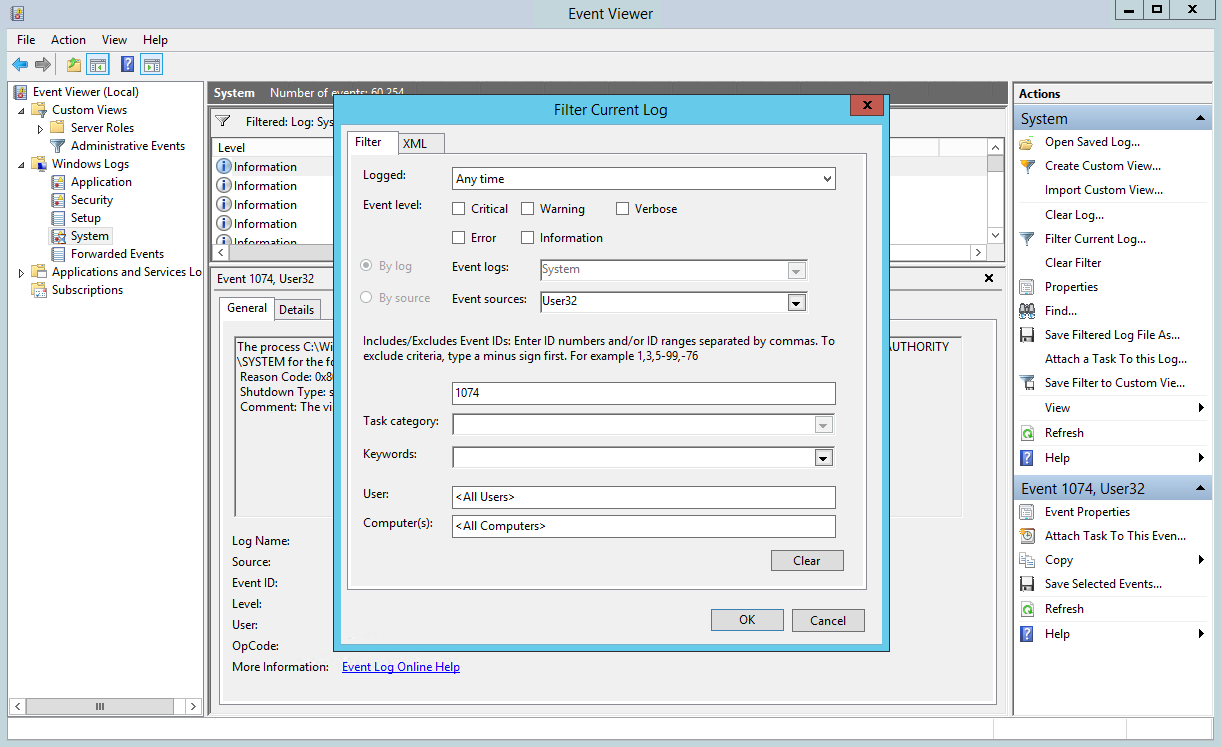
In our case, we want to filter on Event Source: USER32.  Then for Event IDs we want to see only 1074.  If you are after unexpected shutdowns, use 6008.  Once that’s in (like the pic on the right), click OK and this will filter the event log based on our requirements. You can scroll through and see what and who initiated a shutdown.


Leave a Reply

More Posts

Thoroughly cleaning up a WSUS server

I was recently tasked with performing a clean-up of some of our servers, removing old files/software installations as well as a clean-up of our WSUS server.  After a quick look I could see that our previous administrator had set it to download Driver updates as well, which was taking up quite a large amount of […]

Veeam File to Tape Job and how to backup up files directly from a Network Share

A customer of ours has a large archive of files located on a NAS device (around 15TB worth) that they want to simply push off to tape and then remove from the NAS. Network drives don’t show up in Veeam whilst creating backup jobs, so we needed a way to get this working. We use […]

Bypassing Anti-Spam on an Exchange 2007/2010 Receive Connector

I was looking at an old Exchange environment that was being used to send bulk mail outs. We noticed every now and again a bunch of e-mails would not be getting sent, trawling through Message Tracking Logs we could see that the messages were failing because of an AGENT FAIL which usually means that there […]